Configuration & Provisioning
Create the Configuration File
Create a folder named config next to your Floating Server binary.
Inside this folder, create a file named default.yaml.
config/default.yaml
Use the following template:
database:
 # if using sqlite
  type: sqlite
  path: ./data/db.sqlite
# if using sqlcipher
  type: sqlcipher        # <-- switch from sqlite to sqlcipher
  path: ./data/app.db
  password: "your-password"
# if using Microsoft SQL Server
   type: sqlserver
   host: localhost
   port:            # port on which your SQL Server instance is running
   user: floating_user
   password: fs_password
   name: FloatingServerDB
   CryptoProviderKey: ""      # secret used to encrypt db data in OAuth mode
# if using postgres
  type: postgres
  host: localhost
  port: 5432
  user: fsuser
  password: fspassword
  name: fsdb
  sslmode: "disable"   # options: disable, require, verify-ca
  sslrootcert: "/path/to/sslcert/ca.crt" # ignore if sslmode: "disable"
  CryptoProviderKey: "" # secret used to encrypt db data in OAuth mode

# Comment out or remove the fields for the database type you are not using.

server:
  port: 8080 # port on which the server runs
  Verbose: true # level of information given in logs
  BasePath: "" # path prefix of the server
  DisableUserAuth: false # disable user authentication requirement, not admin!
  LogDestination: ""   # path to log output file (e.g. "./logs/app.log").
  TLSCertFile: ""/ TLSKeyFile: "" # Paths to a TLS certificate and private key. When both are set, the server serves HTTPS directly (TLS 1.2 or later), without a reverse proxy. Leave empty to serve HTTP. From v2.7.0.
  TrustedProxies: [] # Reverse proxies the server trusts to report the client's IP address. Default: loopback only. Add your proxy if it runs on another host or container. From v2.7.0.
  EnableSwagger: false # Set `true` to serve the Swagger page at `/swagger`, for example during development. Default: `false`. From v2.7.0.
  SessionMaxAge: 168h # How long a login session lasts before the user must log in again. Default: `168h` (7 days). From v2.7.0.

cloud:
  UseOAuth: false
  # if authenticating with API/Shared key
  APIKey: ""
  SharedKey: ""
  # if authenticating with OAuth
  ClientId: ""
  ClientSecret: ""
  # cloud server config
  BaseURL: "" # default: "https://api.licensespring.com"
  APIPrefix: "" # default: "/api/v4/"
  ServerPublicKey: "" # default: LicenseSpring Prod's public key
  # if having Airgap licenses, fetch this key from platform
  AirgapPublicKey: ""
  # provisioning config
  UseHardwareKey: false # choose provisioning method
  HardwareKeyPIN: "" # optional, custom PIN
  PrivateKeyPath: "" # path to generated priv key. Ignore if using hardware key
  CertificatePath: "" # path to cert received from LS
  SyncIntervalMinutes: 0    # can be skipped, default is 0.
  SyncIntervalHours:   1    # can be skipped, defulat is 1.
DisableSync: false # can be skipped, default is falseCloud sync interval configuration
You can control how often the Floating Server syncs with LicenseSpring Cloud by configuring two options under the cloud section of the server configuration file:
SyncIntervalHoursdefines the number of hours between syncs.SyncIntervalMinutesdefines the number of additional minutes between syncs.
The server combines these values into a single sync interval. The total interval must be between 5 minutes and 24 hours. If the configured values fall outside this range, the server will reject the configuration and log an error indicating that the interval must be between 5 minutes and 24 hours.
Database Configuration
The database section defines how the application connects to the underlying database. Two database types are currently supported: SQLite and PostgreSQL.
SQLite
If you're using SQLite, provide the file path for the database file:
type: sqlite path: ./data/db.sqlite
SQLCipher Integration
Starting from v2.1.0, we offer full encryption of the SQLite database. To enable it:
In your config file, set the database type to
sqlcipherinstead ofsqlite.Before running the server, install SQLCipher on your system (Linux or Windows) and ensure your app links to it.
Installing SQLCipher
Linux
Windows
If you’re on Win 10 or above, install WSL on Windows and run:
PostgreSQL
Update the default.yaml file with the following:
Fields:
host: ThePostgreSQLserver address (usuallylocalhostfor local development)port: Port number (default is5432)user: The PostgreSQL usernamepassword: The password for the specified username: The name of the database to connect to
type: postgres host: the posgres host port: the postgres port user: the user in db password: password name: give the db a name
Setting Up PostgreSQL (Local)
Install PostgreSQL (if not installed)
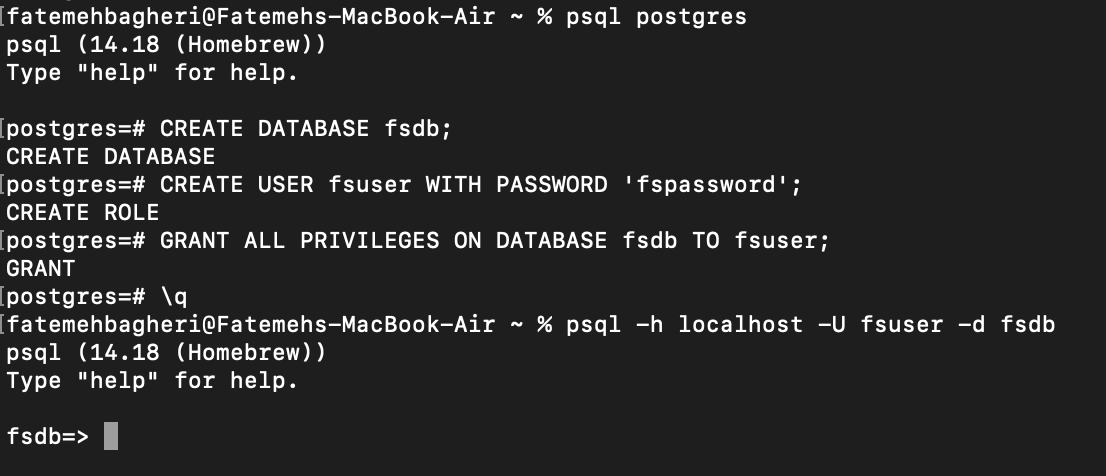
Create the database and user: run
psql postgresthen, inside the psql prompt:
Verify the connection:
You will be prompted to enter the password you set for the database user (for example, fspassword).
This process in MacOS is shown in the image below.
CryptoProviderKey
CryptoProviderKey is a secret key you may use to encrypt data before storing it in the database.
Server Configuration
Port: Network port the server listens on.
Verbose: Set
truefor development logs,falsefor production.DisableUserAuth: Only set true for testing; this disables user authentication for license management features.
BasePath: Starting in v2.3.0, you can configure Floating Server to serve under a path prefix by setting
BasePath. WhenBasePathis set (for example,/licensing), the server will be reachable at:http://<host>:<port>/<base-path>.
Logging
By default, the Floating Server writes its log to sdk.log in the same folder as the executable. If it can't write there, it writes sdk.log to the current working directory instead.
To write the log somewhere else, set LogDestination in the config file to the path of the log file.
To send logs to standard output instead of a file, for example when running in a container, set the environment variable:
LOG_OUTPUT=stdout
Set Verbose: true for detailed development logs, or false for production.
Cloud Configuration
API/Shared Keys: Fill
APIKeyandSharedKey.OAuth: Set
UseOAuth: trueand provideClientId,ClientSecret, andCryptoProviderKey.If your
BaseURLorAPIPrefixdiffers from the defaults, specify them in the cloud section. You must also provide the server’s public key in the following format:
Provisioning the Floating Server
Provisioning ensures that only authorized instances of the server are allowed to run.
Starting with Floating Server v2.2.0, provisioning can be completed using either:
Hardware Key authentication (YubiKey), or
The previously supported certificate-based method (CSR)
Both provisioning options are available and managed through the LicenseSpring Platform. This section provides a high-level overview; detailed steps for each method are outlined below.
Floating Server Provisioning with Certificates (CSR)
Image: Provisioning the Floating Server
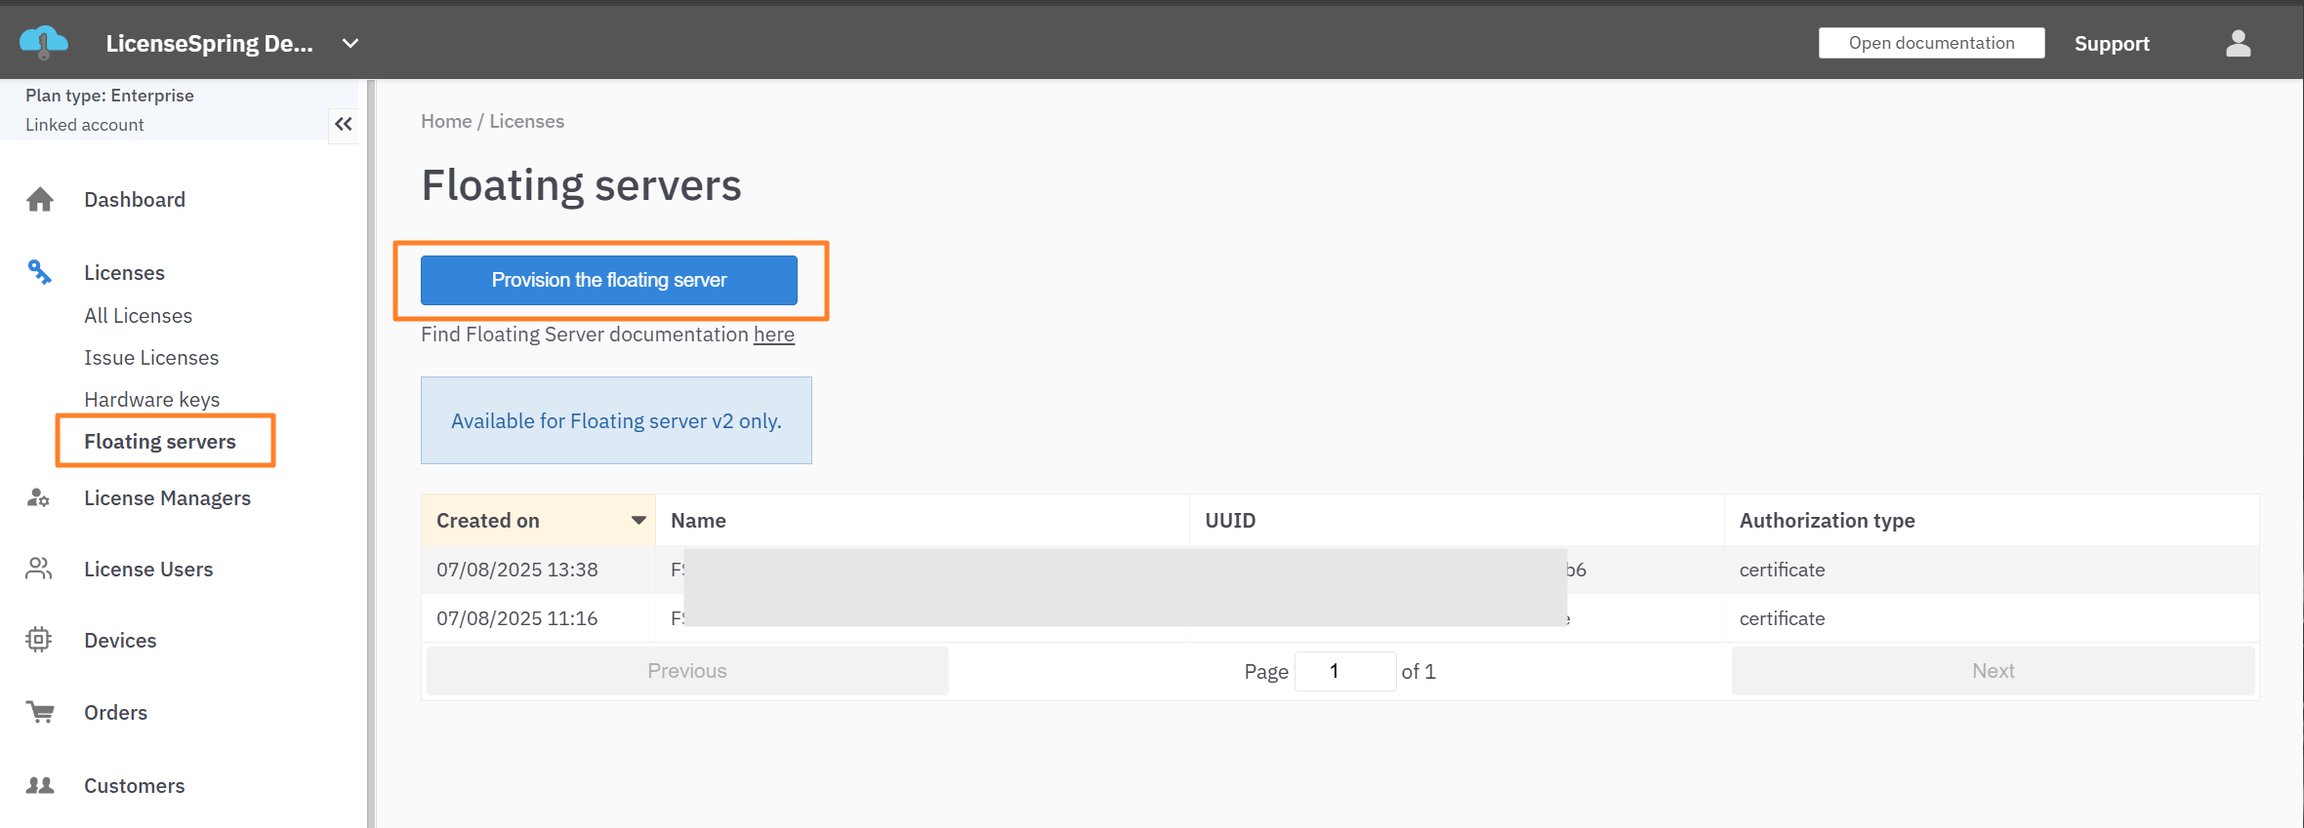


Once you select Edit Config File, as shown in the image above, you can define the Floating Server settings, including the port and sync interval. The port (default: 8080) can be customized to match your network setup. The sync interval determines how often the server communicates with LicenseSpring Cloud and is configured using SyncIntervalHours and SyncIntervalMinutes, which are combined into a single interval. This interval must be between 5 minutes and 24 hours; otherwise, the configuration will be rejected.
Floating Server Provisioning Using a Hardware Key
As an alternative to certificate-based provisioning, the Floating Server can be provisioned using a hardware key (dongle). This method authorizes the server based on the presence of a physical security device connected to the machine. When a hardware key is enabled, the Floating Server workflow remains largely the same as in the previously described examples, with the added requirement of a connected hardware key.
Use this option when physical enforcement or offline licensing is required.
Optional: Set a Custom Hardware Key PIN
Before starting the provisioning process with a hardware key, you may choose to update the default hardware key PIN. If you set a custom PIN, ensure that the new value is included in the Floating Server configuration file, as shown below.
Configuration for Hardware Key Provisioning
When provisioning with a hardware key, update the configuration file (default.yaml) accordingly:
To use a YubiKey with the Floating Server, set the UseHardwareKey configuration value to true. When this option is enabled, the server detects the hardware key and establishes the connection during startup.
Requirements
A supported hardware key (YubiKey)
Hardware key drivers installed on the server
Hardware key physically connected to the Floating Server machine
Required permissions to perform this action
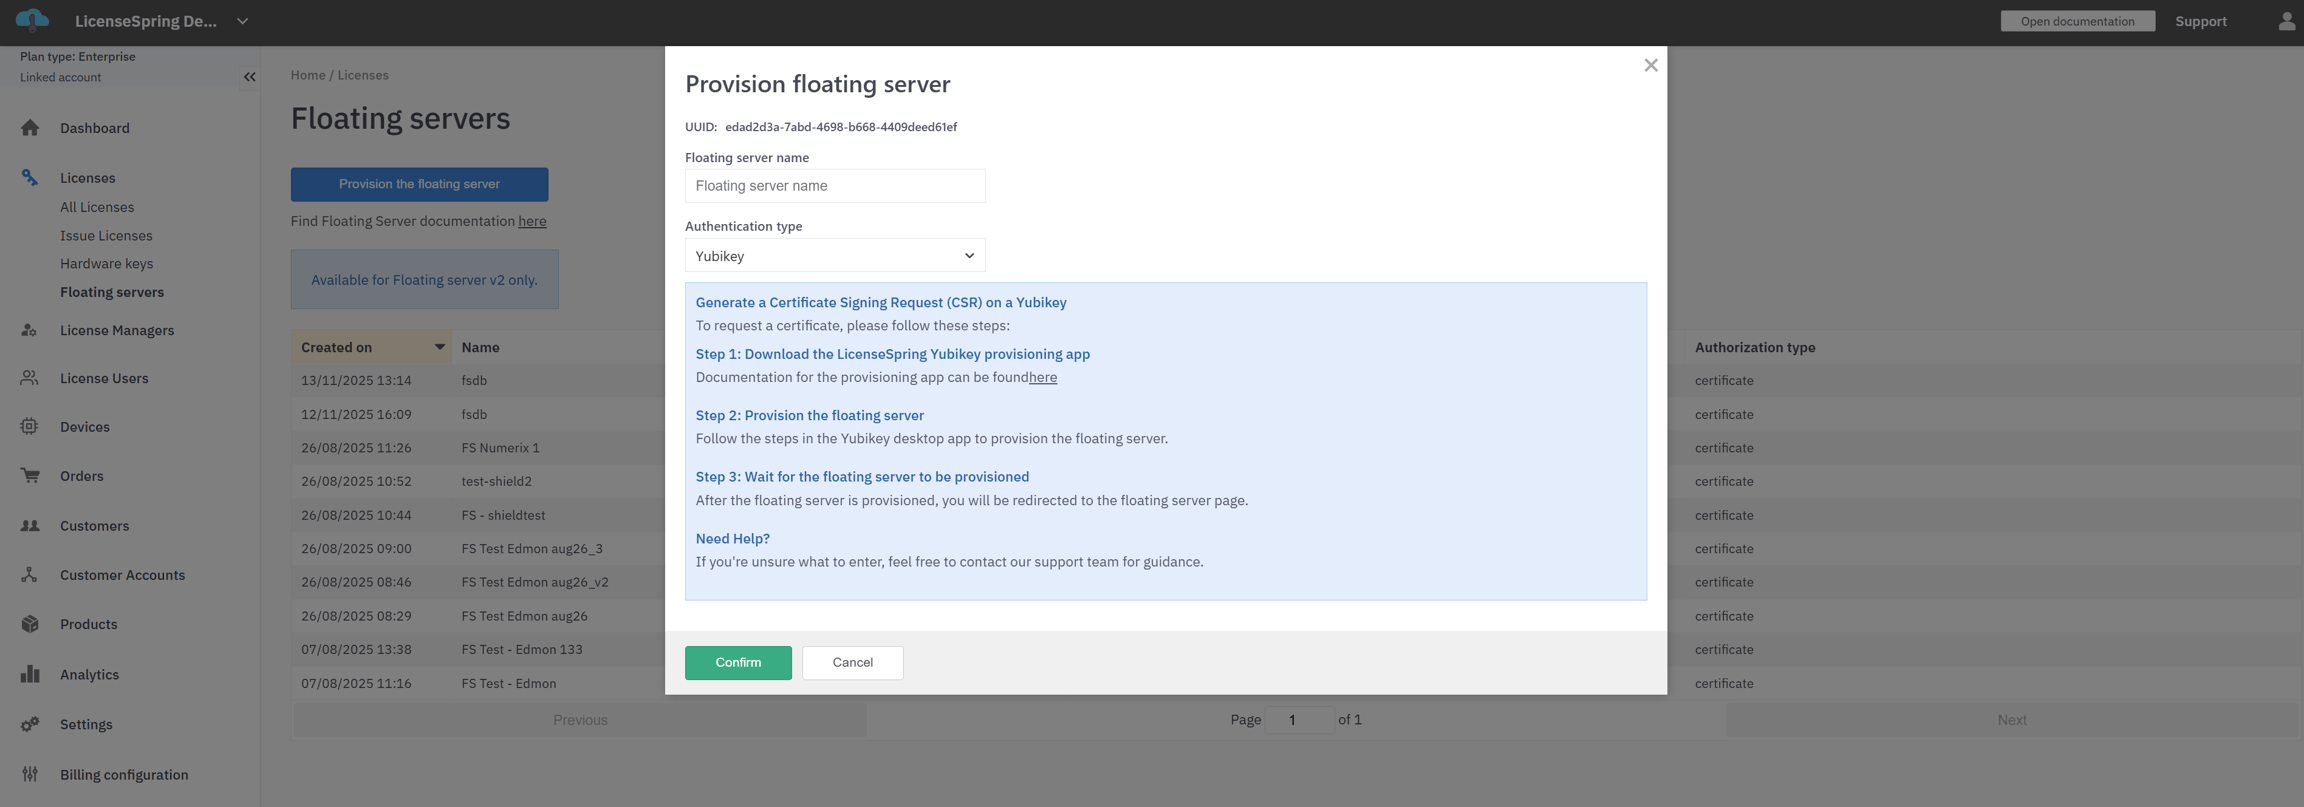
Provision the Floating Server:
Open the LicenseSpring Platform
Navigate to → Licenses → Floating Servers
Click Provision the Floating Server
Enter a server name
Select Hardware Key as the authentication type
Follow the steps in the platform UI and click Confirm
Create a License for Hardware Key–Based Floating Server Use
After provisioning the Floating Server with a hardware key, you must create a license that is explicitly enabled for hardware key usage.
When creating or editing the license in the LicenseSpring Platform:
Navigate to Licenses
Create a new license
Enable the Required Hardware Key option (checkbox)
Save the license
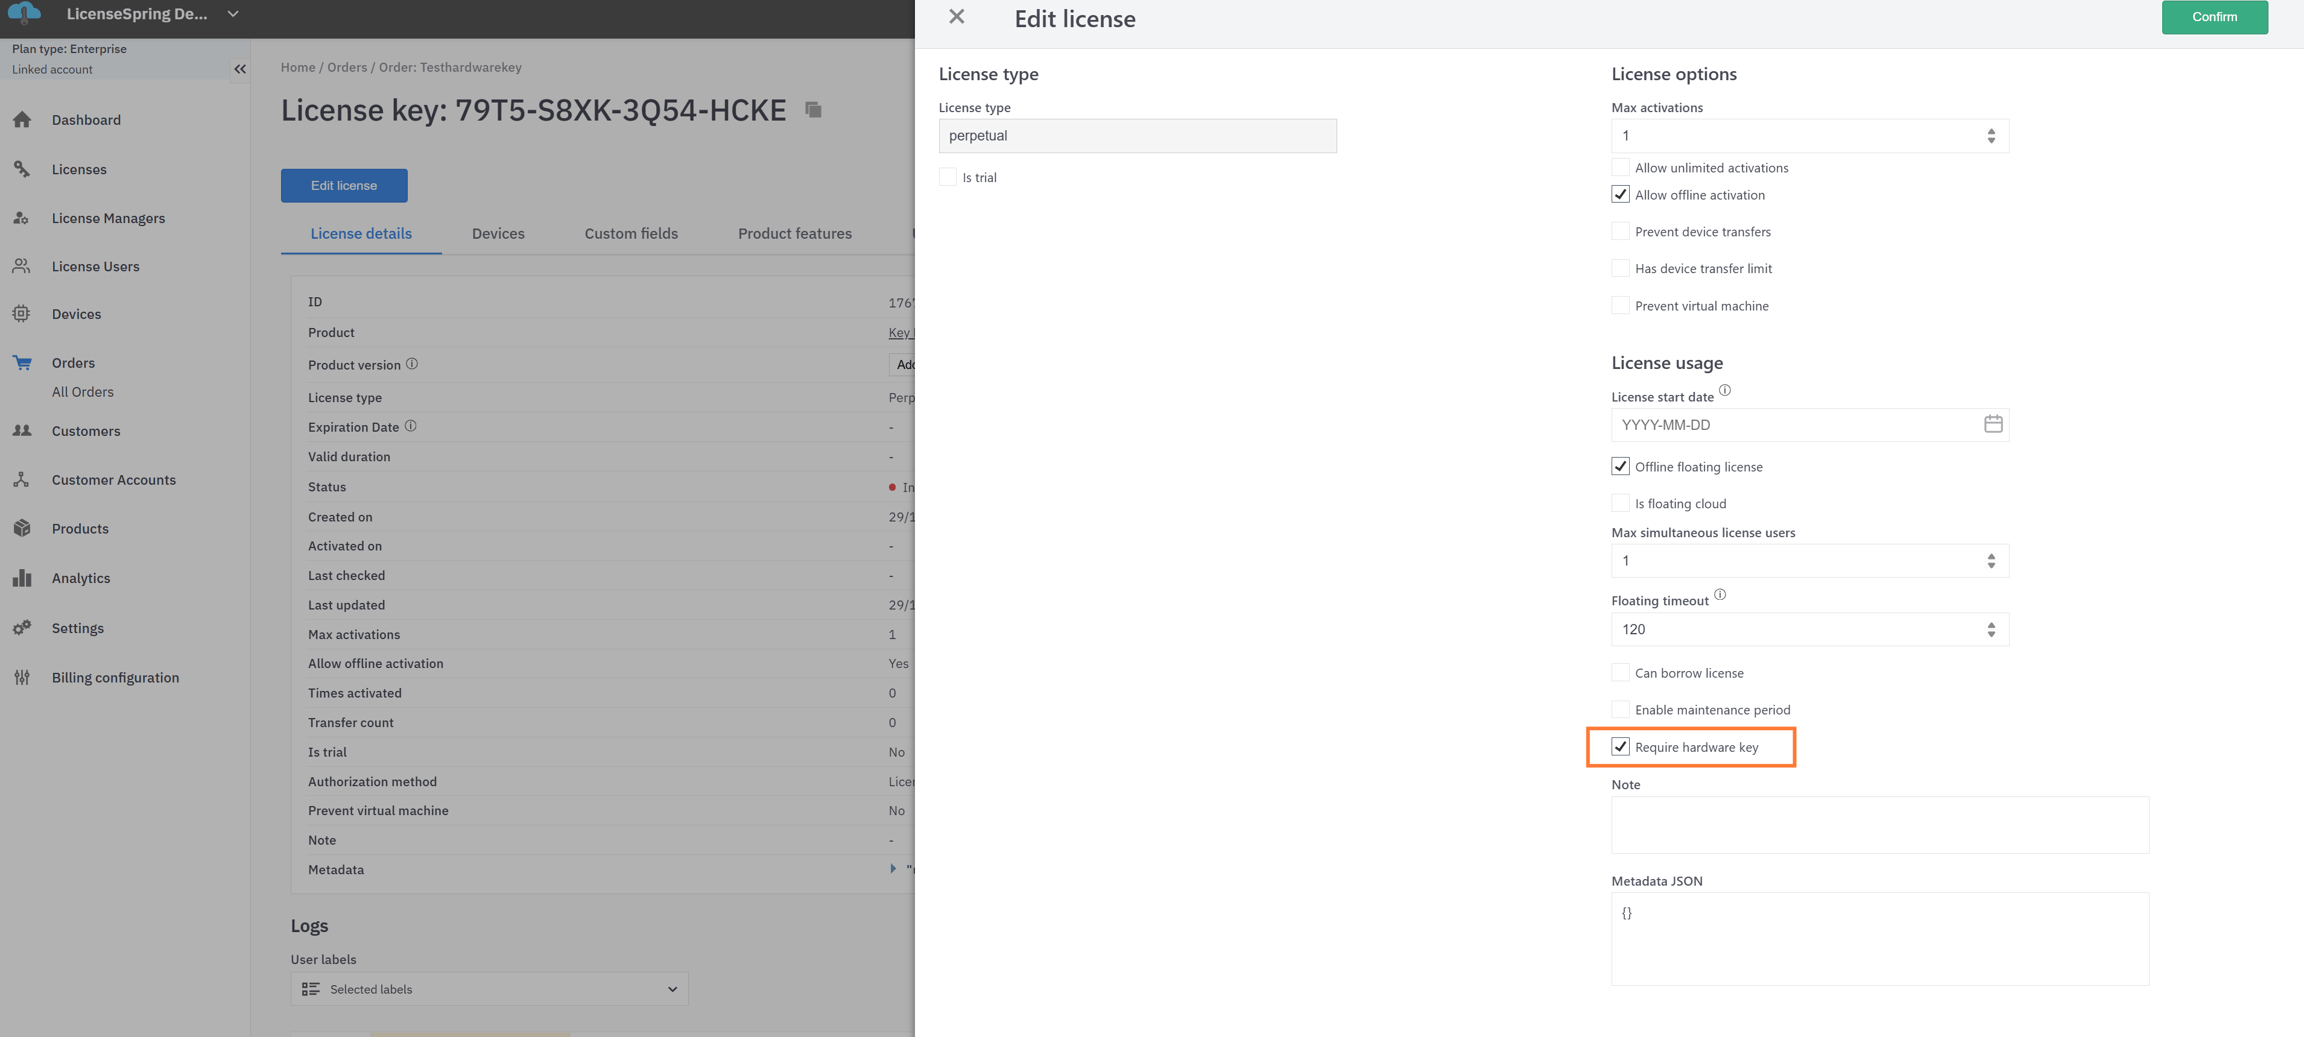
Only licenses with the Hardware Key option enabled can be used with a Floating Server that is provisioned using a hardware key.
Hardware Key and Server Lifecycle
In Floating Server v2.2.0, the server’s lifecycle is tightly coupled to the hardware key connection:
When the server starts, it establishes a connection to the hardware key.
When the server shuts down, the hardware key connection is closed.
If the hardware key is disconnected while the server is running, the server will shut down gracefully.
Last updated
Was this helpful?